The platform where you follow our analysts’ work.
Findings, fixes, controls and evidence live in one place, with dates. The board sees the overview, and the technical team sees the detail.
What you see
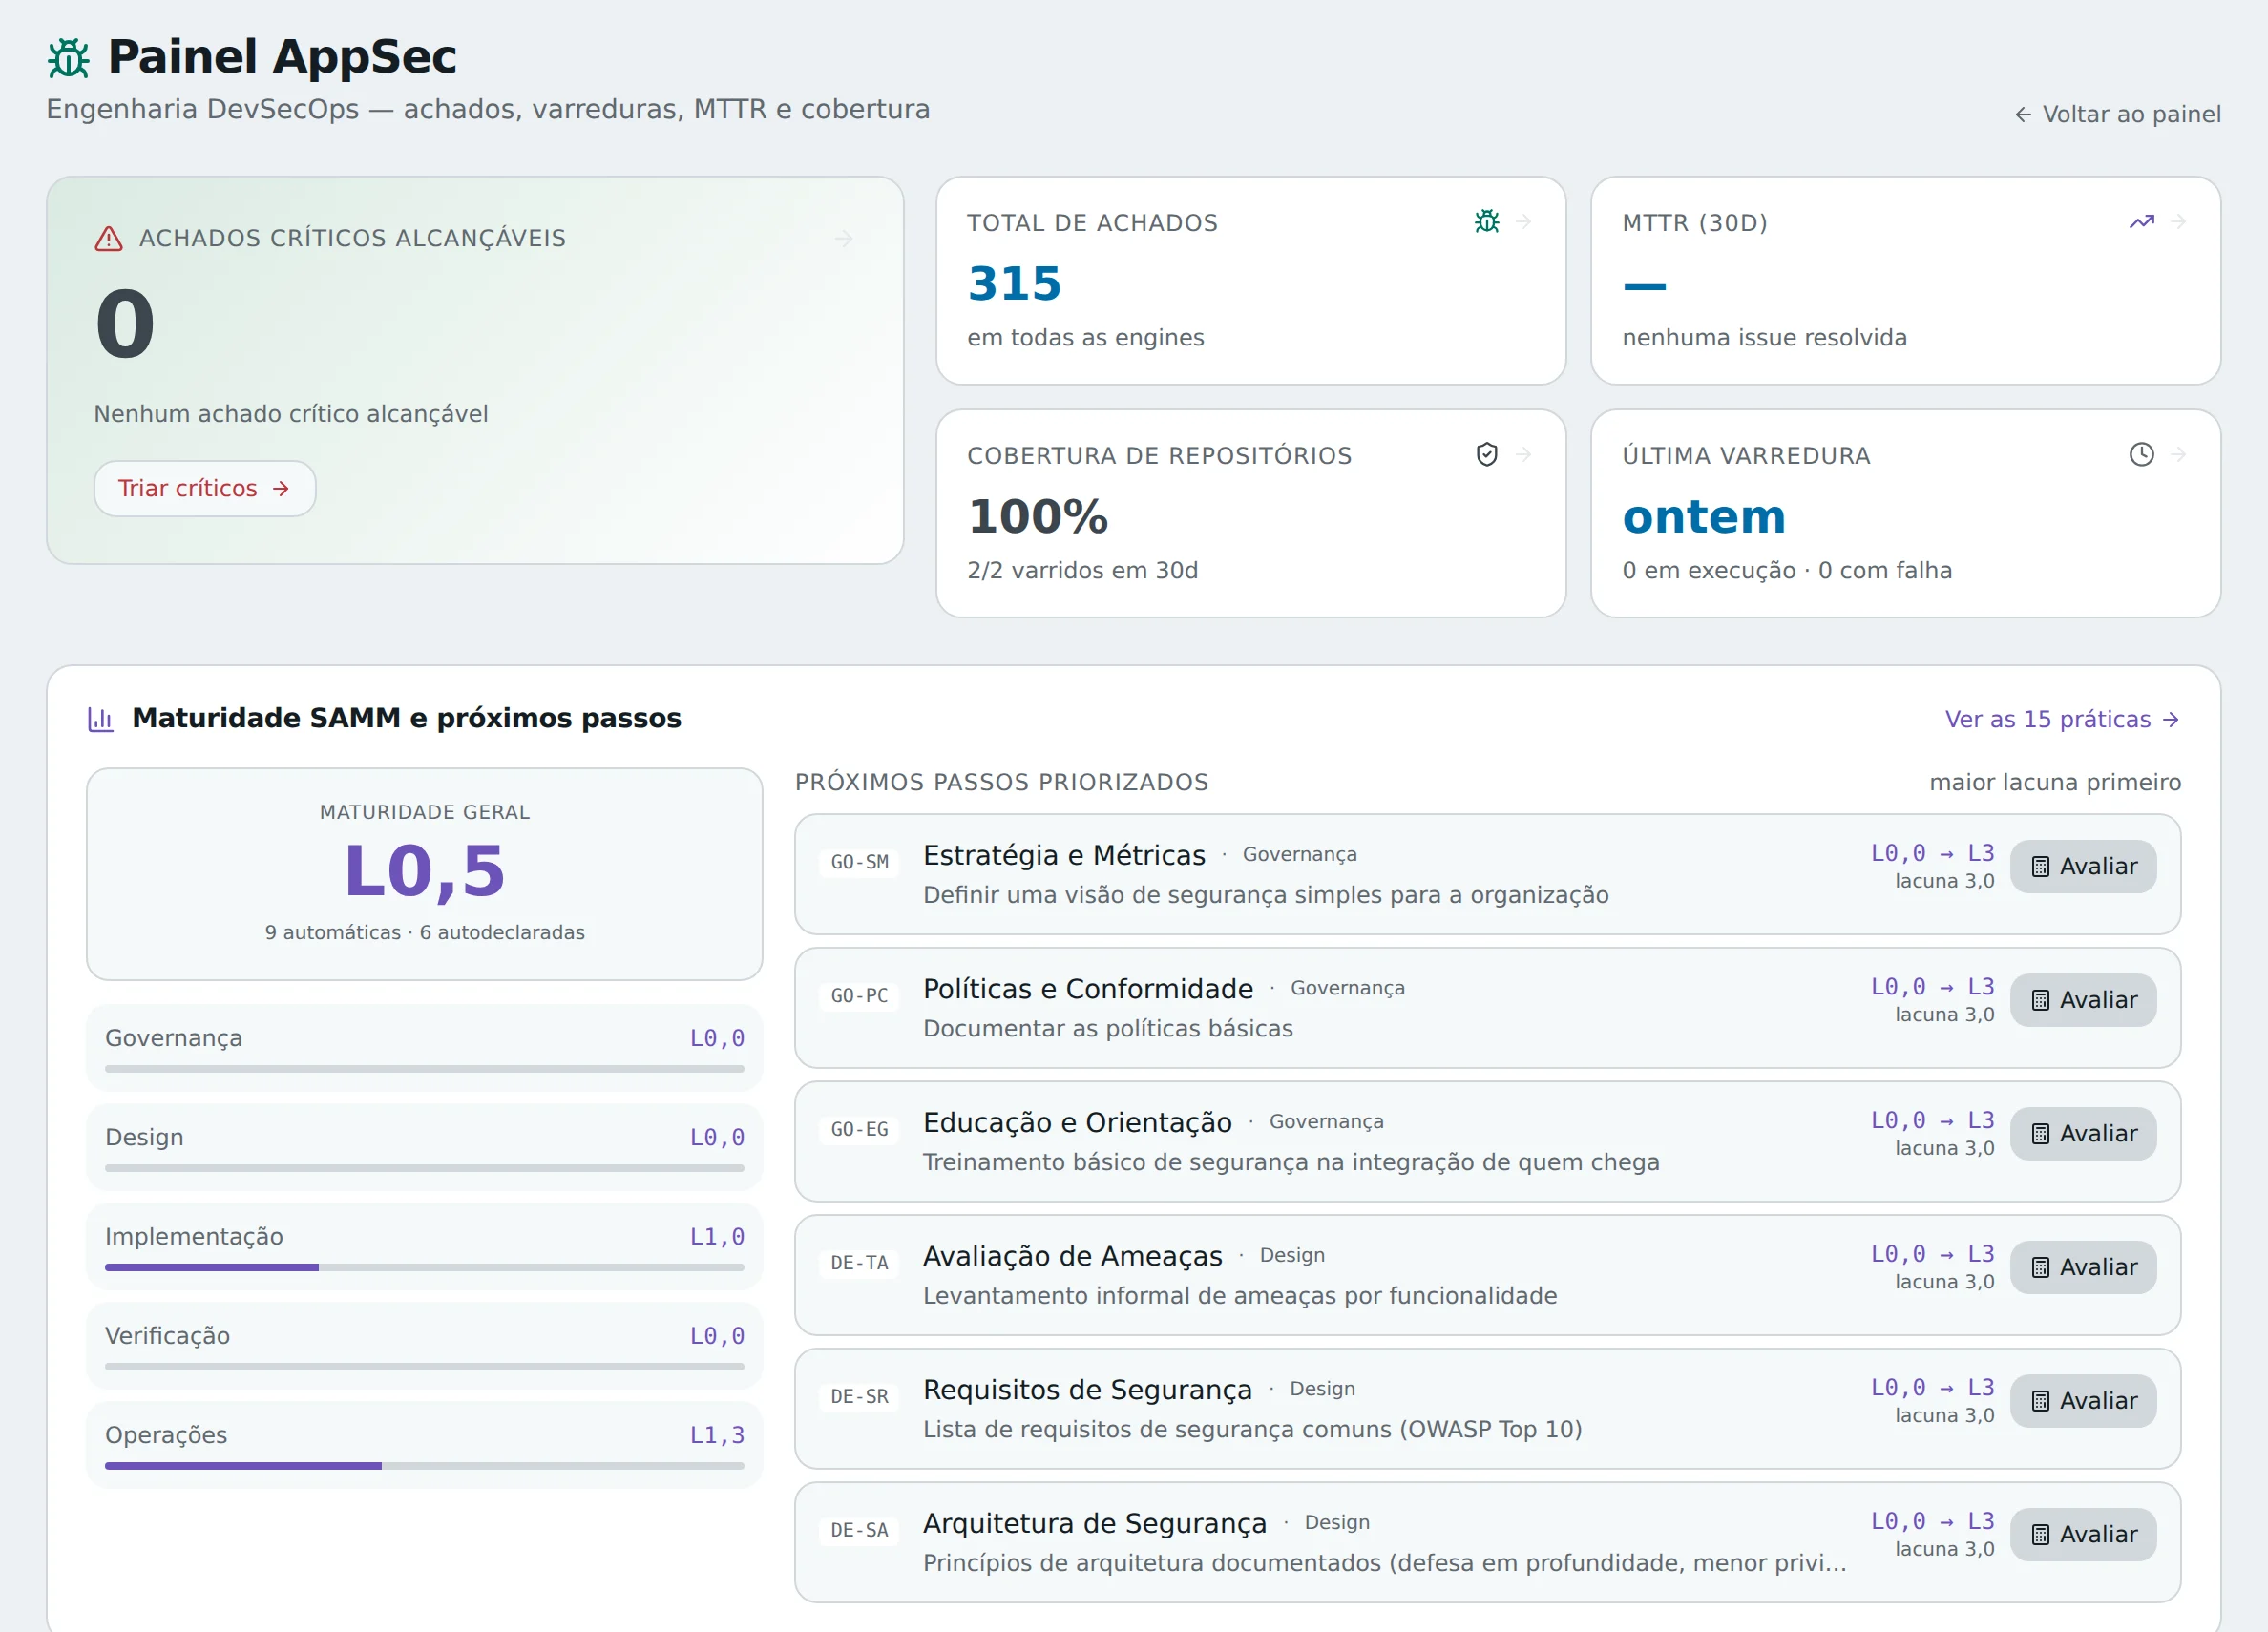
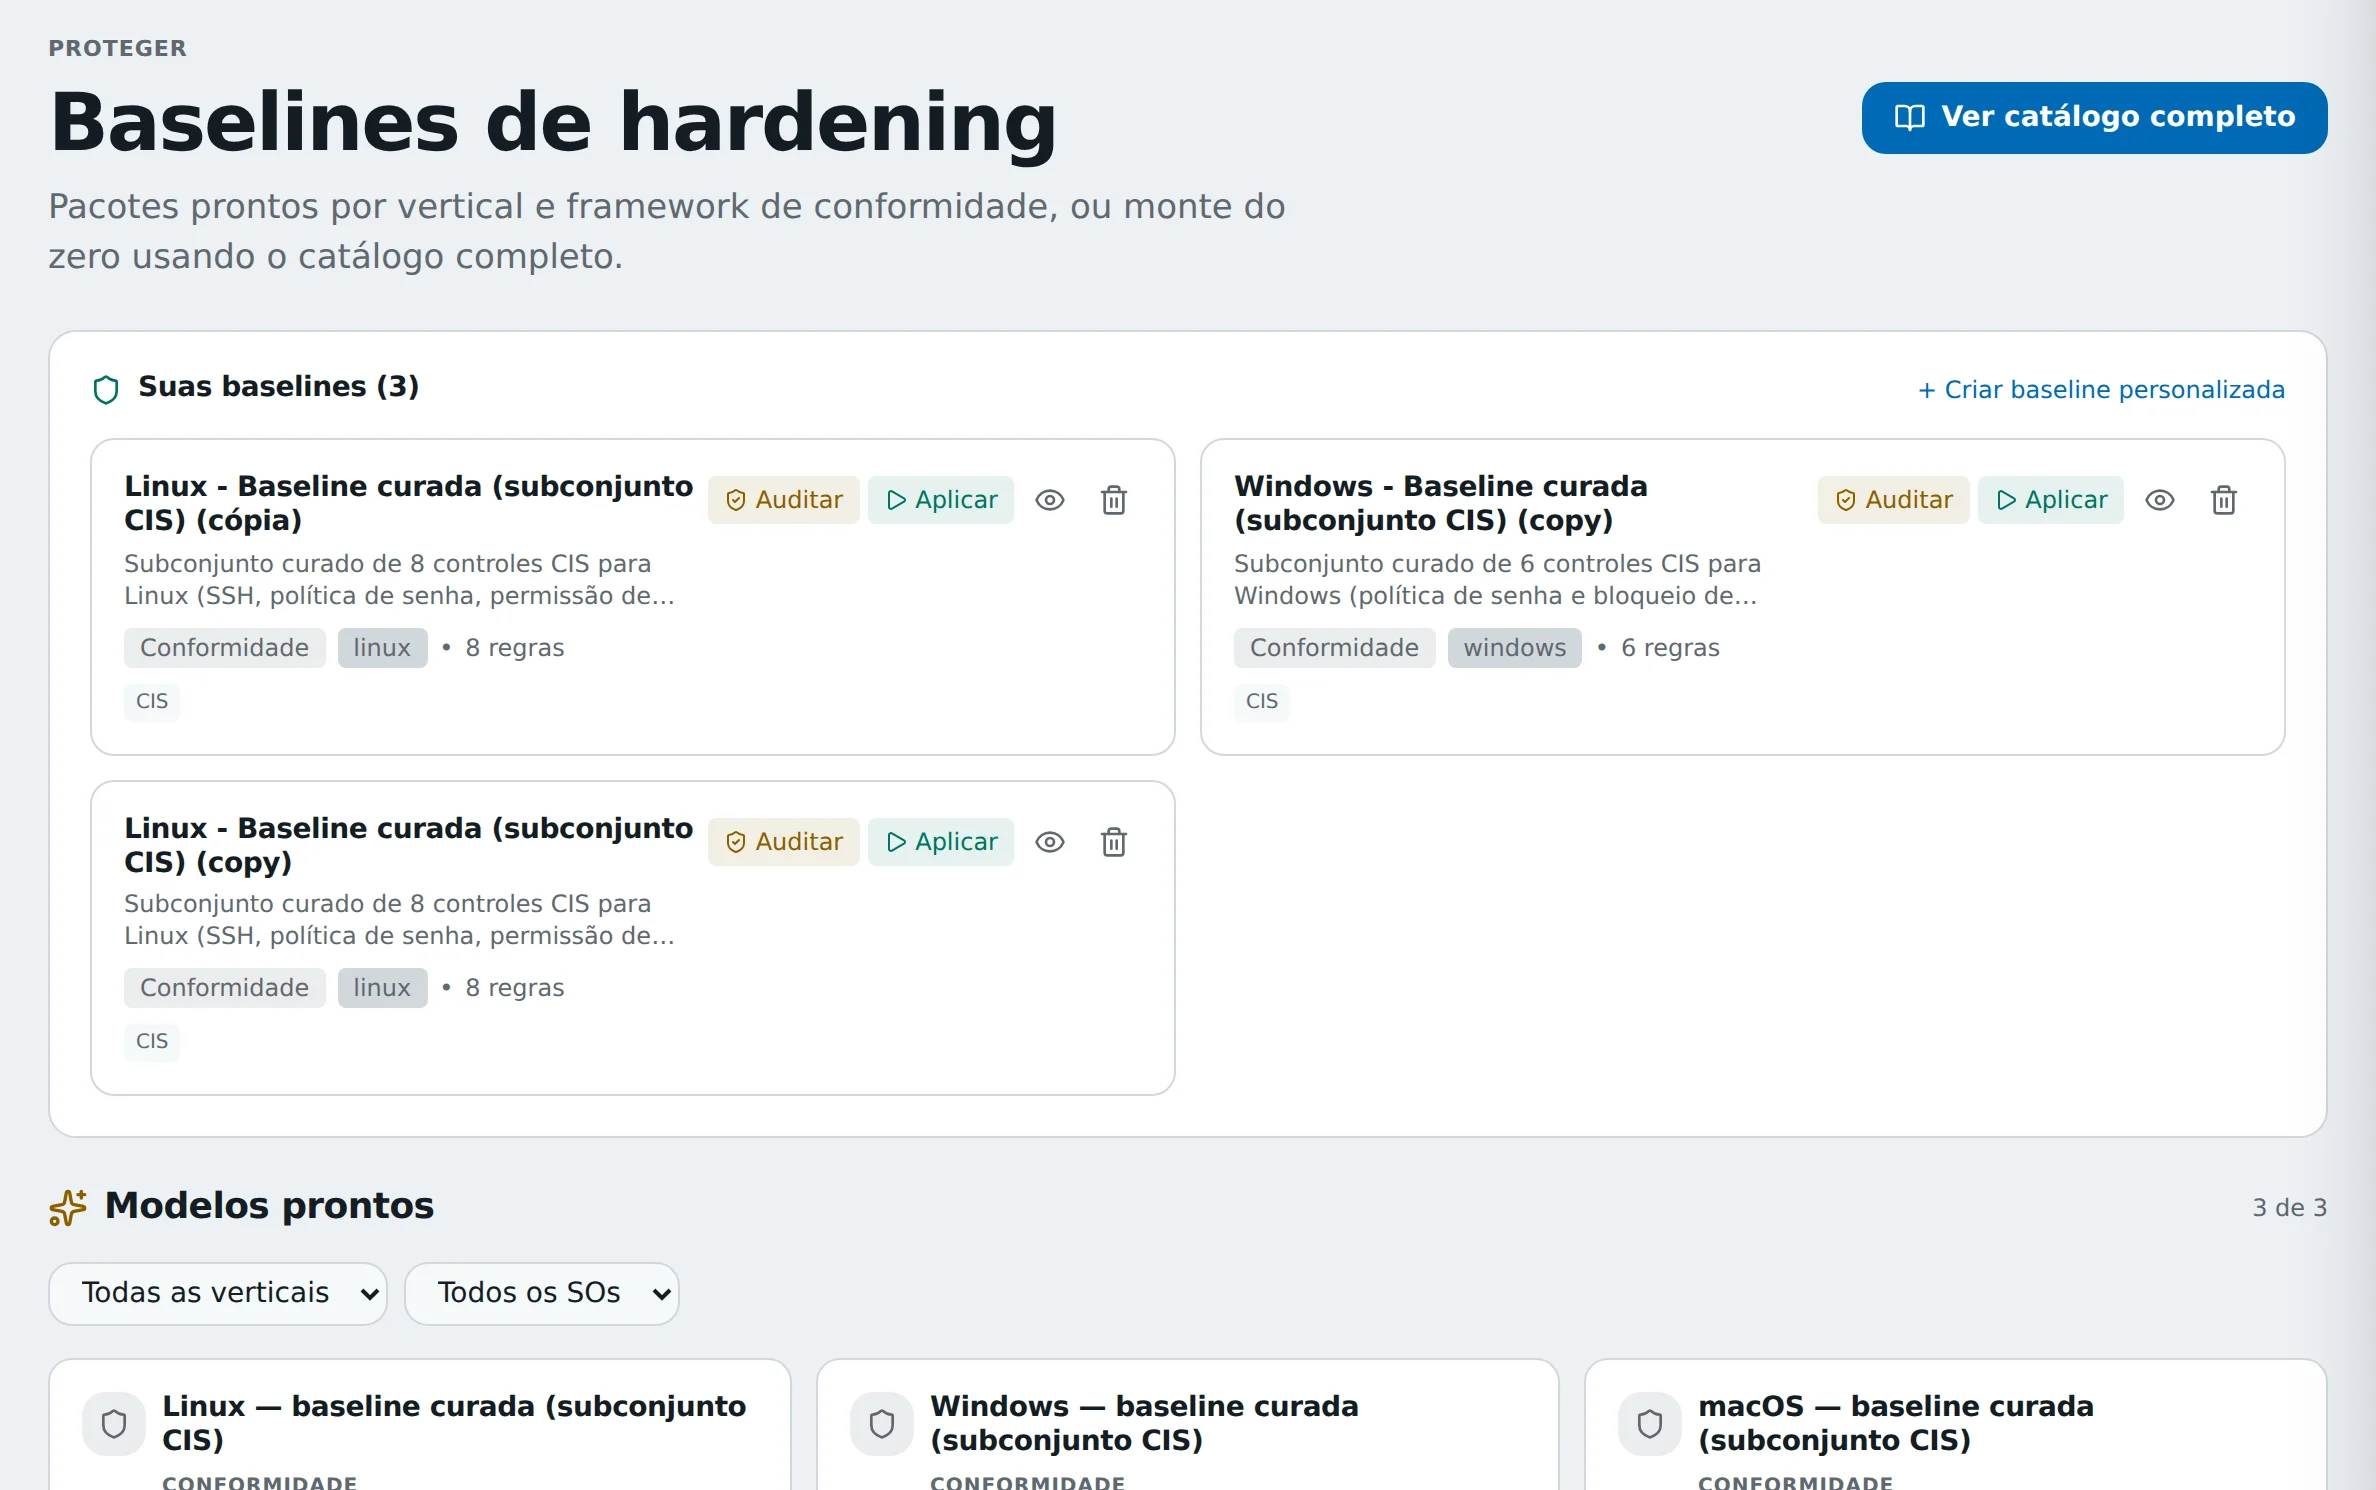
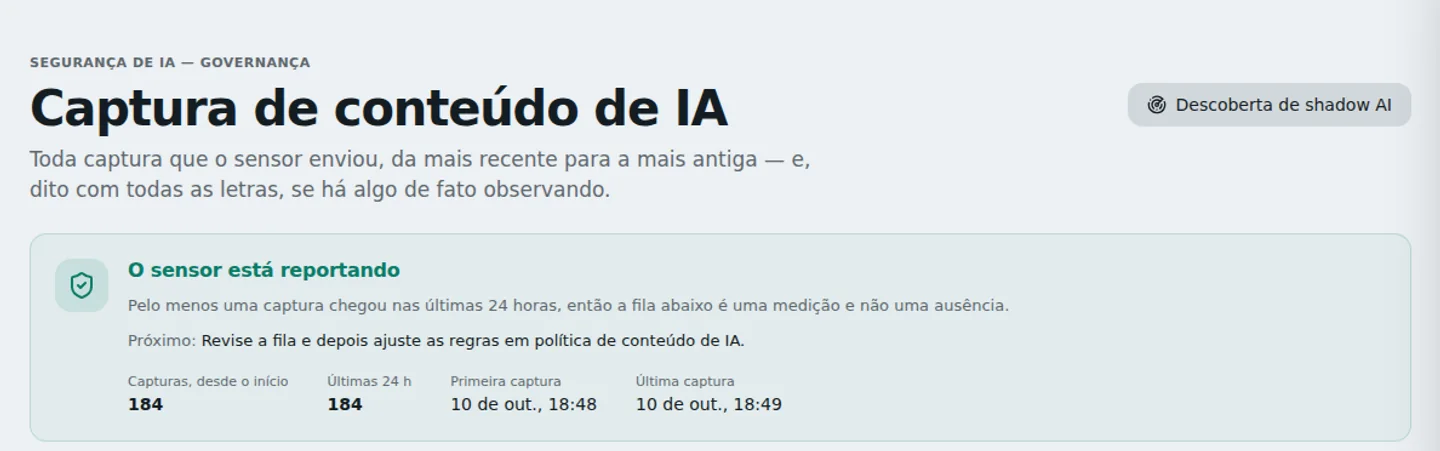
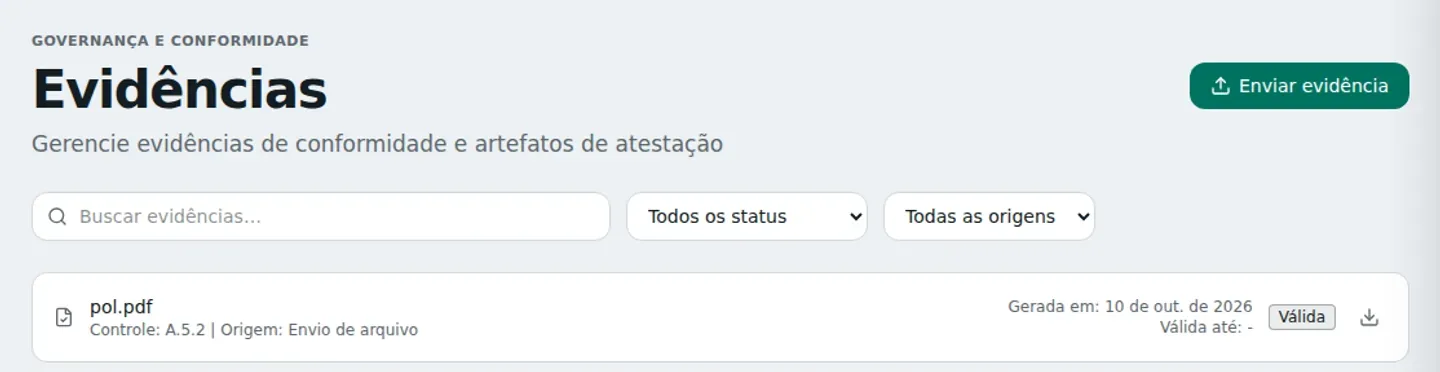
Actual platform screens, from a test account.
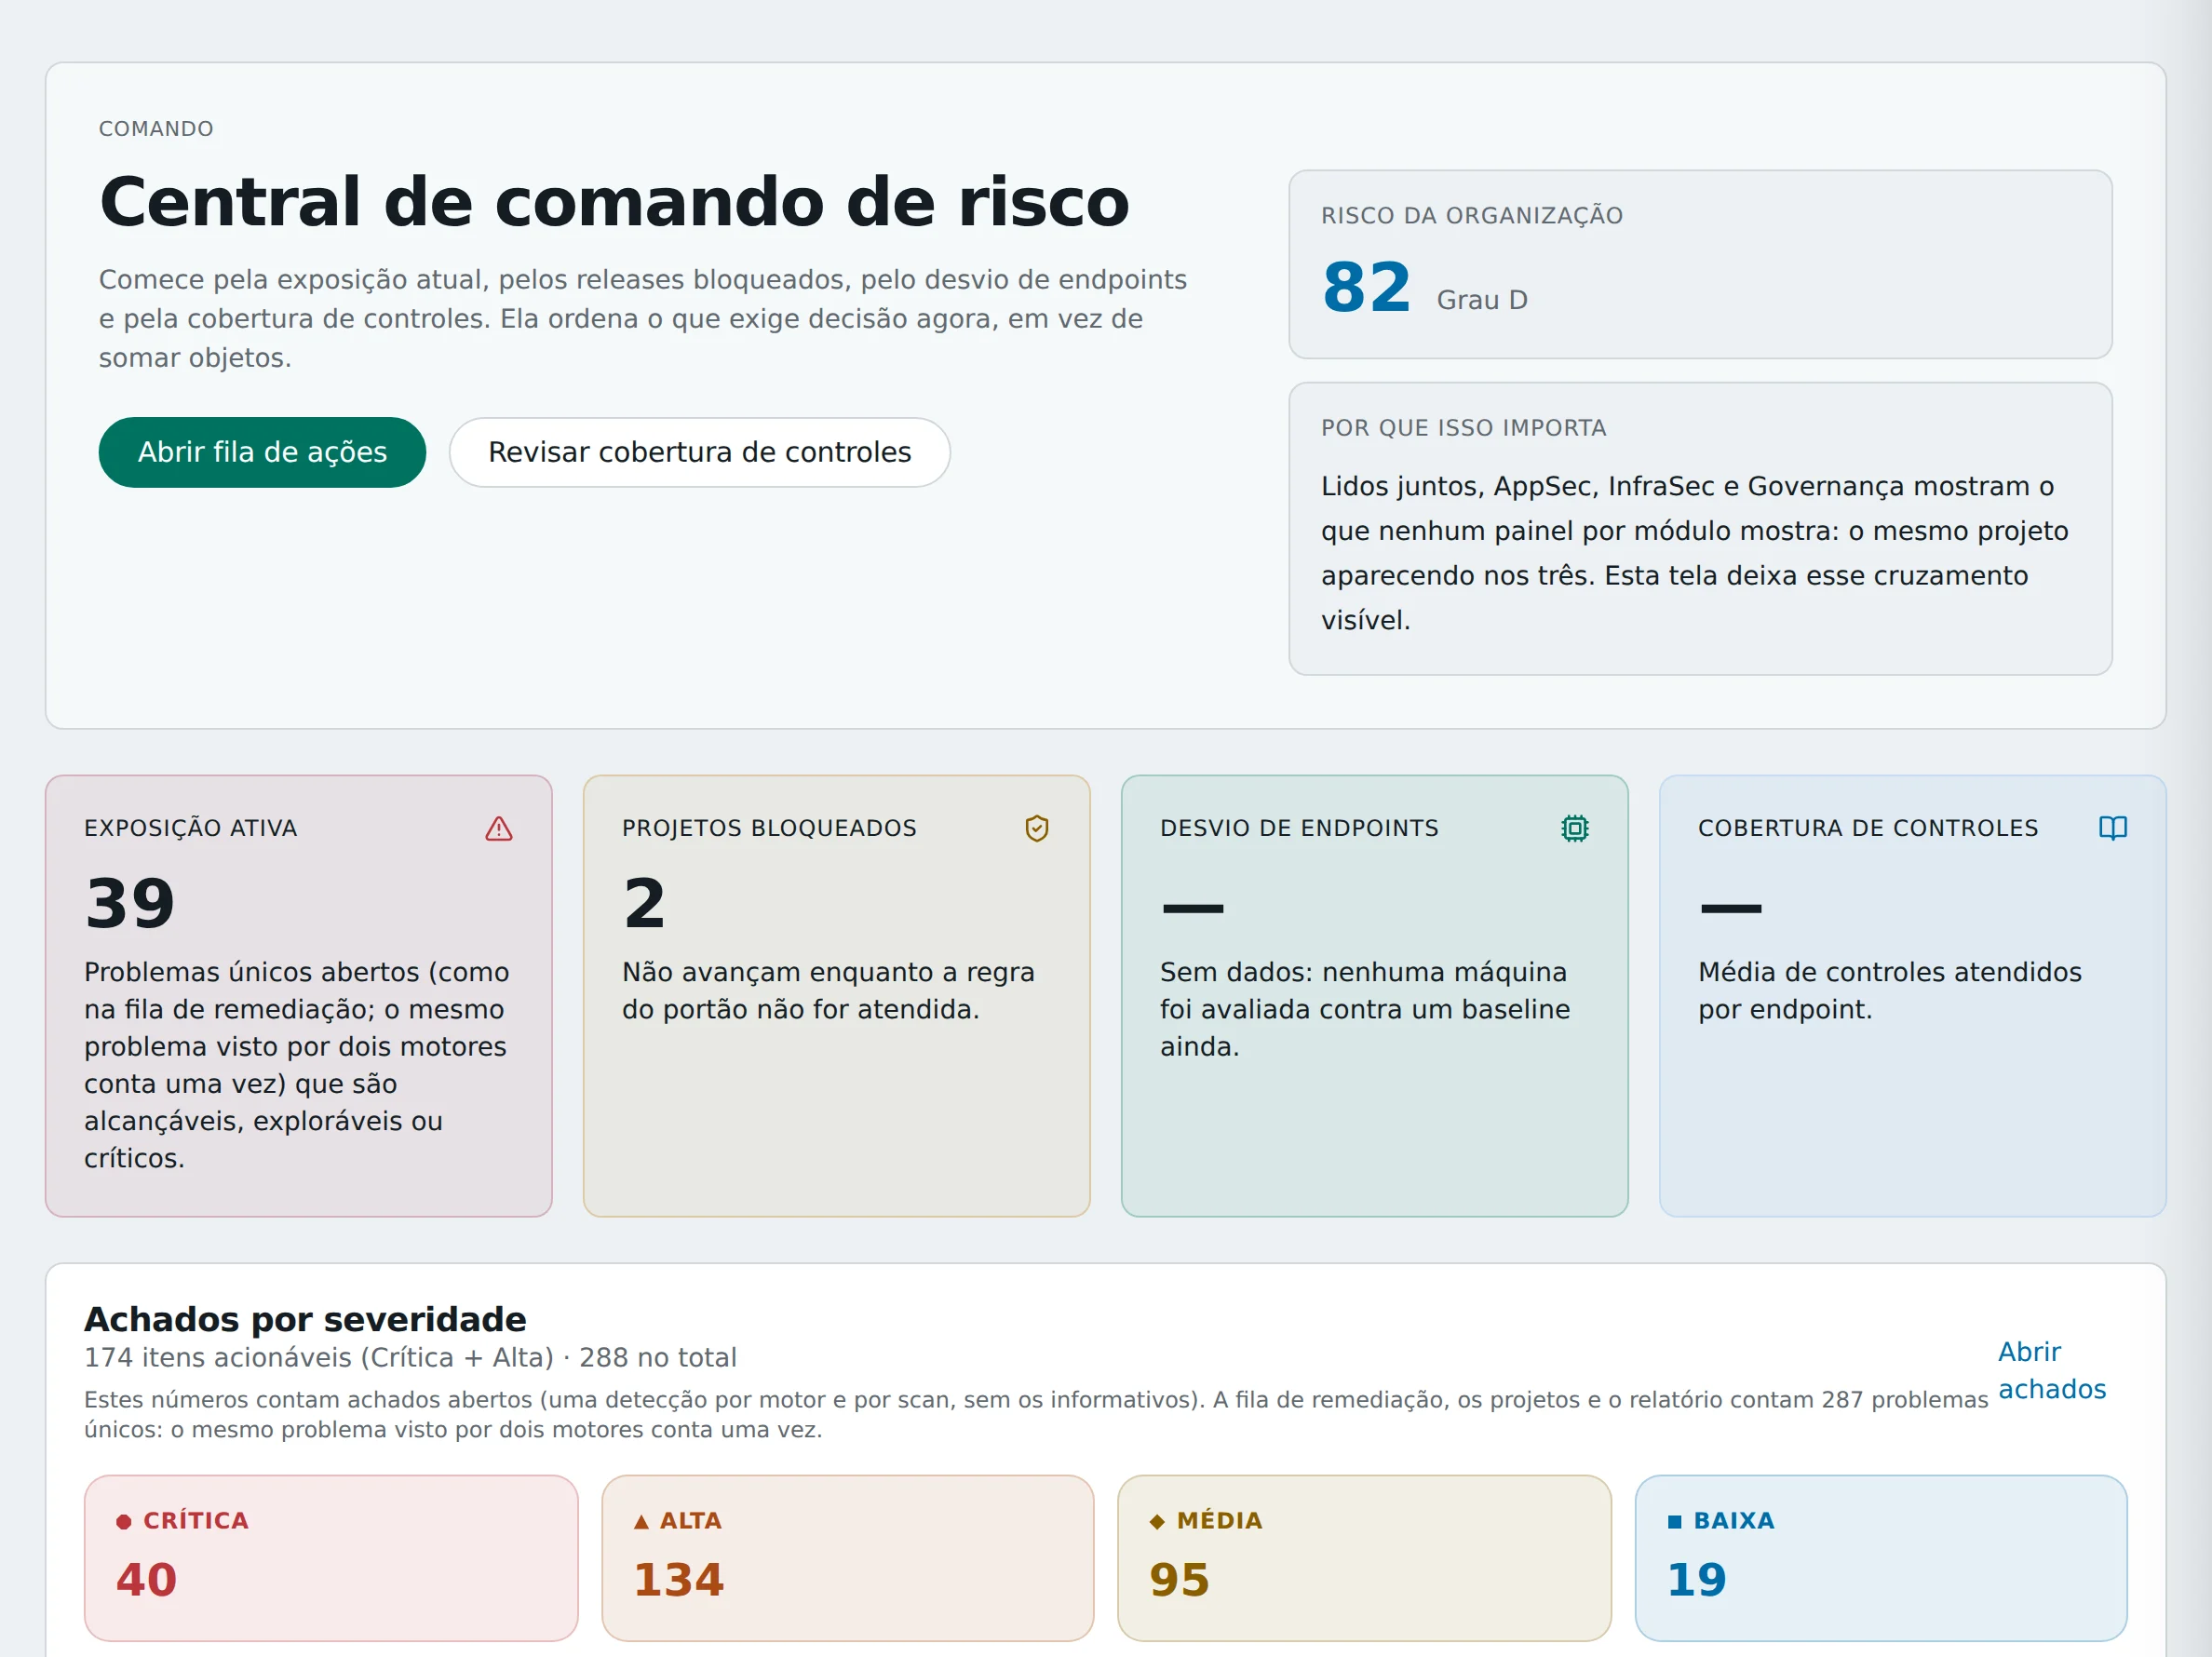
- The organization risk score, from 0 to 100, with its grade. This is the number the board follows.
- Active exposure: open problems an attacker can reach or exploit.
- Blocked projects: software versions that do not ship until the rule is met.
- Findings by severity, from critical to low. The analyst starts with the critical ones.
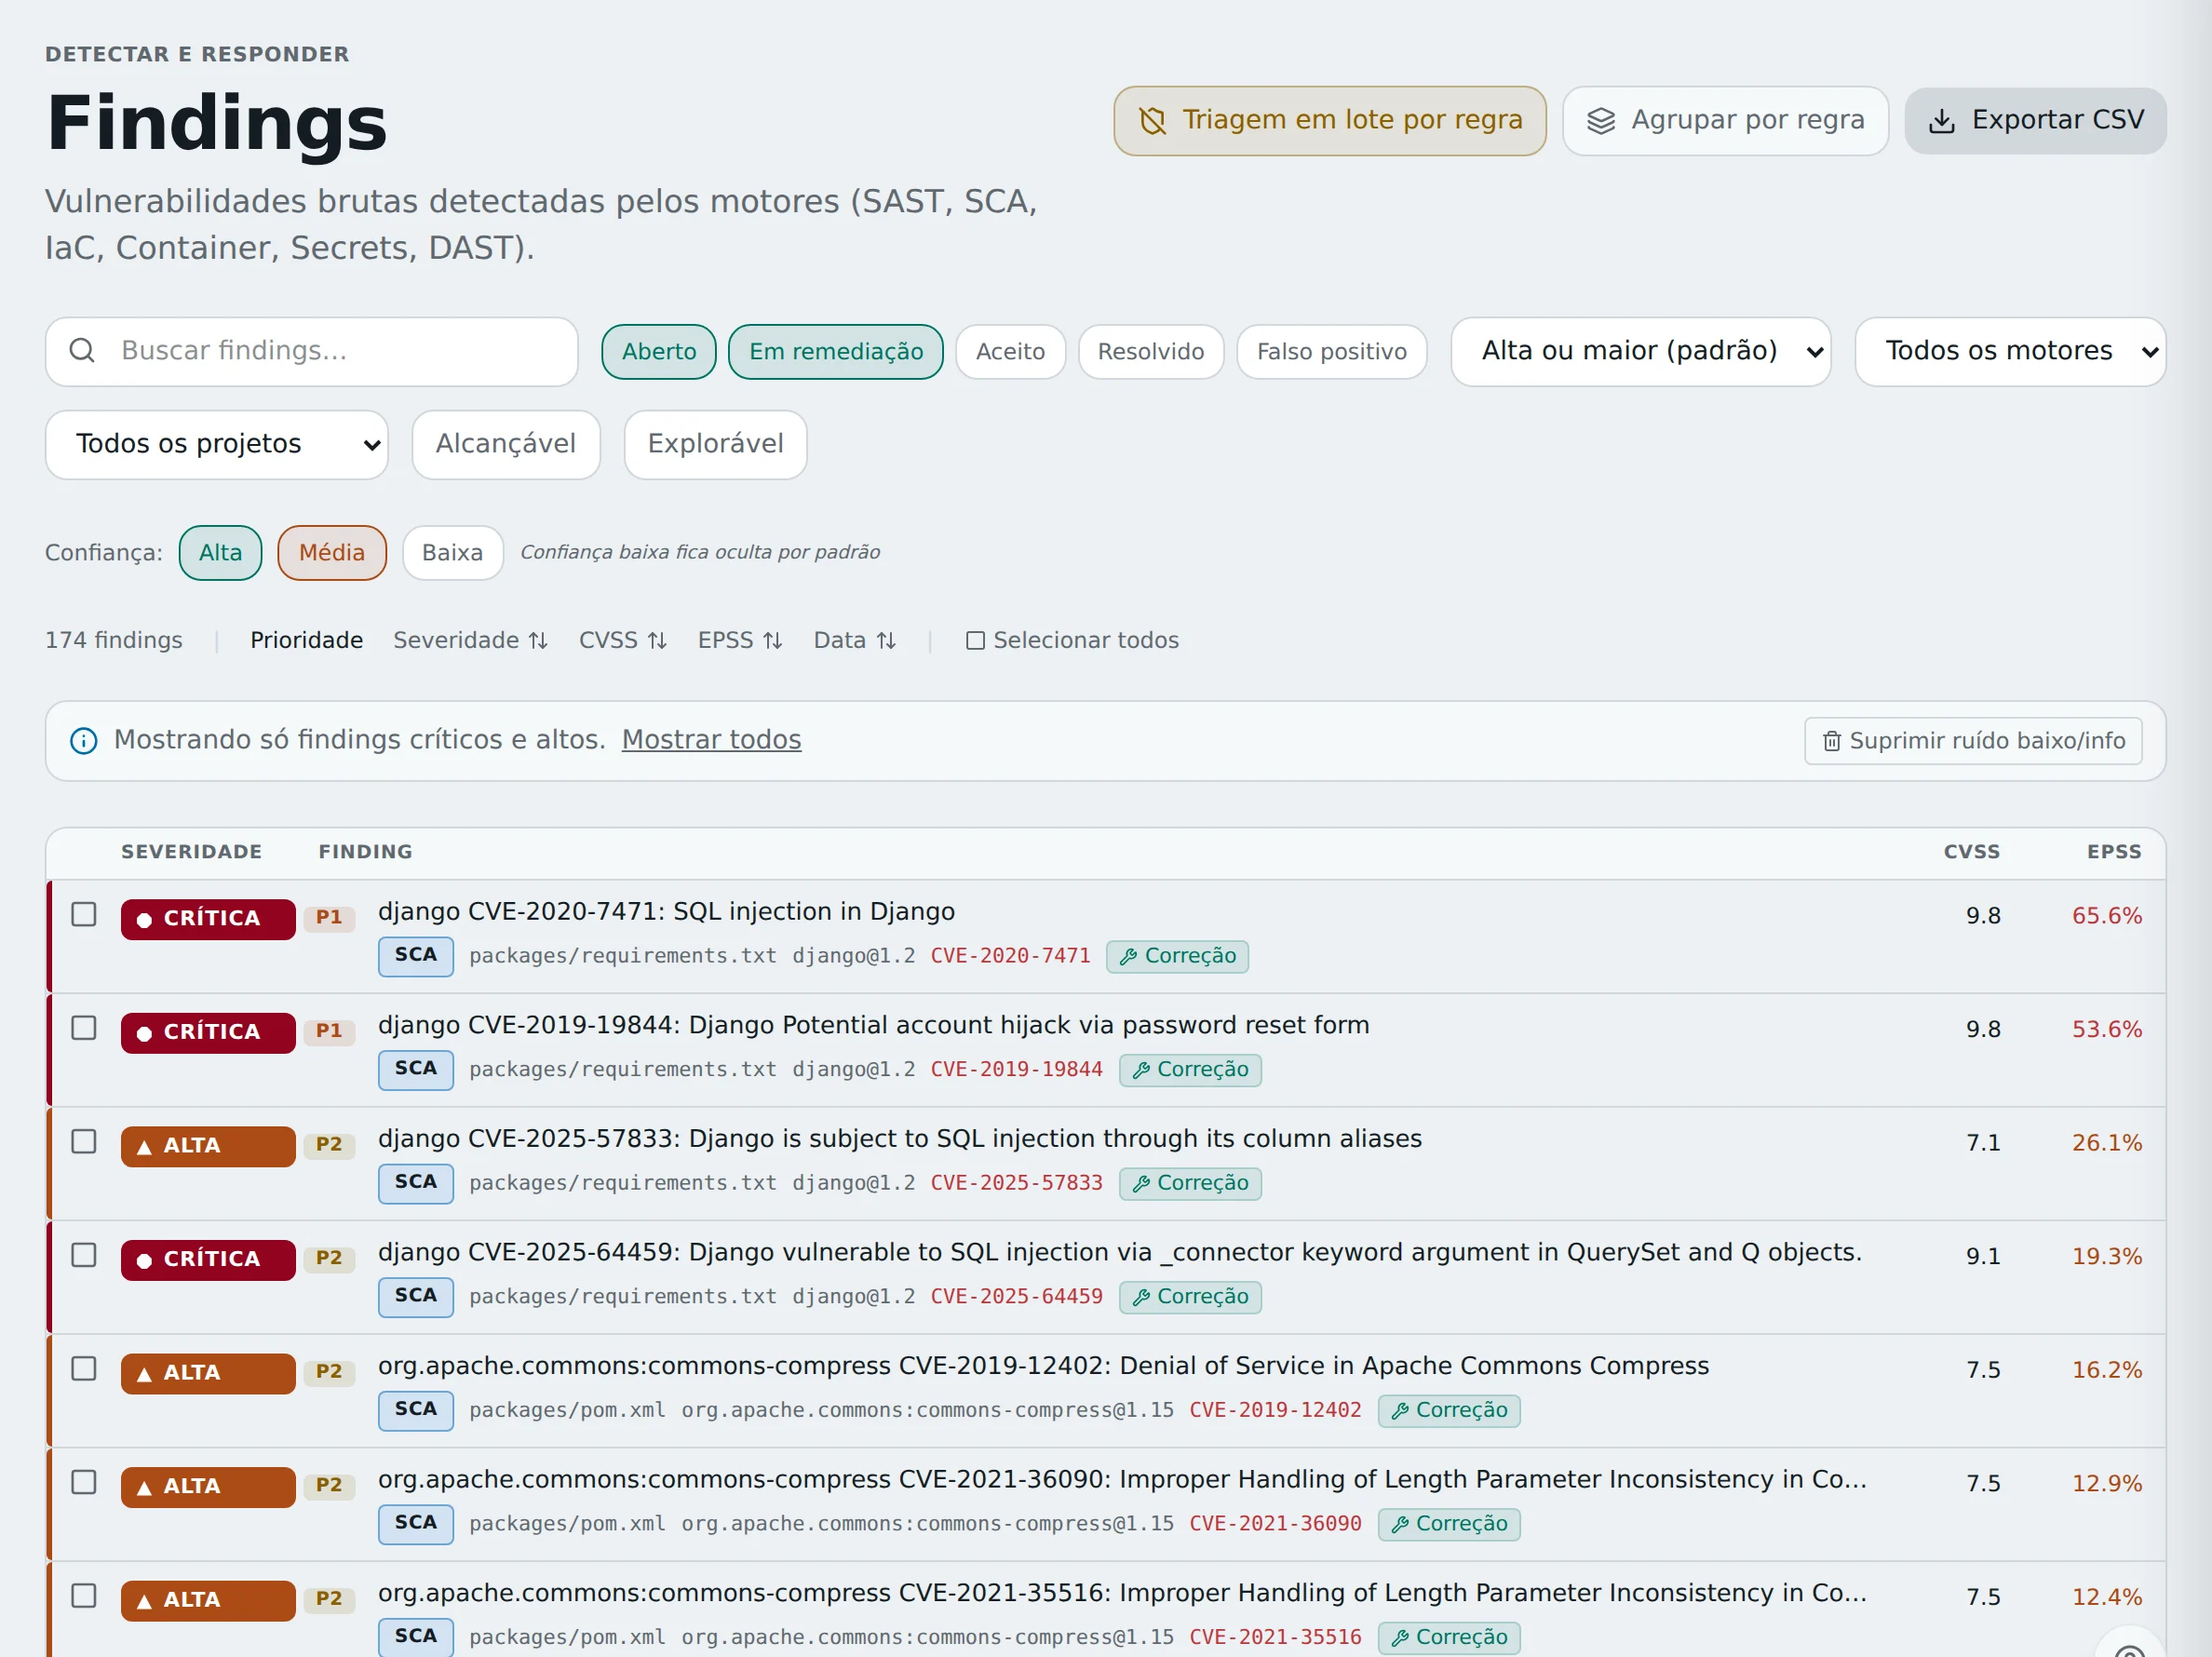
For whoever answers for security
Progress on each area
You see what the analyst did, what is being fixed and what is left, without waiting for the meeting.
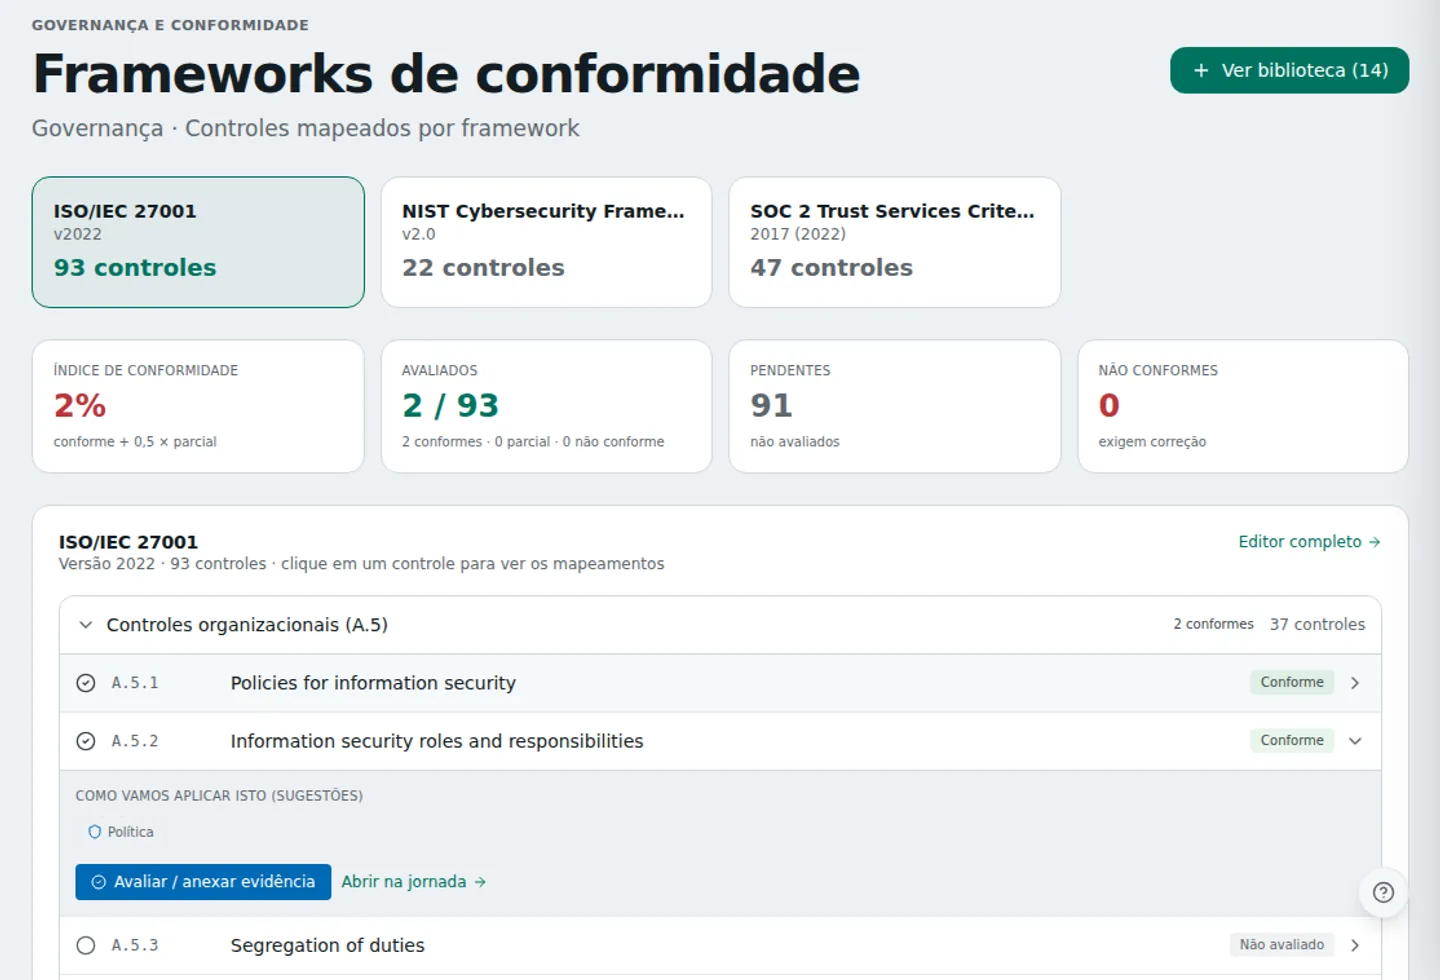
Dated evidence
Each control has its evidence, with the date it was produced. The audit finds everything in one place.
A report the board can read
The executive report comes out of the platform itself, written for the board.
Specification
For the technical team.
| Input formats | SARIF 2.1.0, CycloneDX 1.6, Nessus XML, DAST results and vendor CSV. |
|---|---|
| Software bill of materials (SBOM) | Generated in CycloneDX 1.6 from the analyzed dependencies. |
| Loaded standards | ISO/IEC 27001:2022 (93 controls), SOC 2 (47 criteria), NIST CSF 2.0 and OWASP SAMM v2. |
| Infrastructure agent | Windows, Linux and macOS. |
| Interface languages | Portuguese, English, Spanish, French and Simplified Chinese. |
Talk to a specialist for 30 minutes.
Tell us what your company needs. You leave the call with three priorities for your environment.
Talk to a specialist
Prefer to write? Use the email contato@cyberarmor.com.br.