The platform where every security finding goes from priority to fix.
CyberArmor brings together what your security tools find, shows what to fix first and keeps the evidence of every finding and every exception. The retest result comes in the analyst's addendum. It is the platform Hegeon uses in its consulting projects.
Our work follows
- ISO/IEC 27001:2022
- Public secure configuration benchmarks
- OWASP
- LGPD (Brazil’s data protection law)
Four areas of work
All of them follow the same method and deliver evidence on the same platform.
Secure development
A client asked for proof that your software is secure. Your development team has no security specialist.
- Code and dependency X-ray
- Findings in priority order, with fix guidance
- Application penetration test (pentest)
Infrastructure
Every server was set up a different way. The auditor wants proof of configuration.
- Machine assessment
- Hardening based on public secure configuration benchmarks and your policy
- Monitoring and response under contract, during the agreed hours and SLA
Governance and compliance
LGPD or ISO 27001 now has a deadline. The evidence is scattered.
- LGPD compliance and ISO/IEC 27001 readiness
- On-demand security officer (vCISO)
- Security awareness with phishing simulation
Secure AI use
Employees use AI at work. The board does not know what data goes into it.
- AI use assessment in 30 days
- Inspection of Brazilian personal data and attachments
- Report and AI use policy
To start: fixed projects of 2 to 4 weeks
Designed for small and mid-sized companies. Each project ends with a report and, if it makes sense, a proposal for an ongoing service.
- 30 days
AI use assessment
Shows which AI tools the company uses and what personal or confidential data shows up in them.
Fixed price quoted within 1 business day
- 2 to 3 weeks
Code X-ray
Shows the software flaws an attacker can reach, in priority order.
Fixed price quoted within 1 business day
- 2 weeks
Machine assessment
Compares the configuration of servers and workstations with public secure configuration benchmarks.
Fixed price quoted within 1 business day
Method timelines
- 30 min
- the first call with a specialist
- 2 weeks
- the Machine assessment
- 2 to 3 weeks
- the Code X-ray
- 30 days
- the AI use assessment
- up to 30 days
- to the first awareness campaign
- 5 steps
- from assessment to report, with a deliverable in each
How we work
Five steps. In each one, you receive a concrete deliverable.
Assessment
We learn your environment, the policies your company already has and what the auditor or your client is asking for.
You receive: a picture of the starting point, with the most urgent risks.
Prioritized plan
We order the work by business risk and by the deadline you need to meet.
You receive: the plan with priorities, owners and dates.
Execution by our analysts
An assigned analyst carries out the plan within the rules of your environment. Every action is recorded.
You receive: the fixes applied and the record of each one.
Continuous monitoring
After delivery, we keep watching configuration, vulnerabilities and controls. Your environment changes every week.
You receive: drift alerts and up-to-date evidence on the platform.
Executive report
Each cycle ends with a report written for the board.
You receive: the report and dated evidence, ready for the audit.
You follow the work on the same platform the analysts use.
Every finding, exception and piece of evidence is recorded with a date. When the audit comes, the proof is already organized.
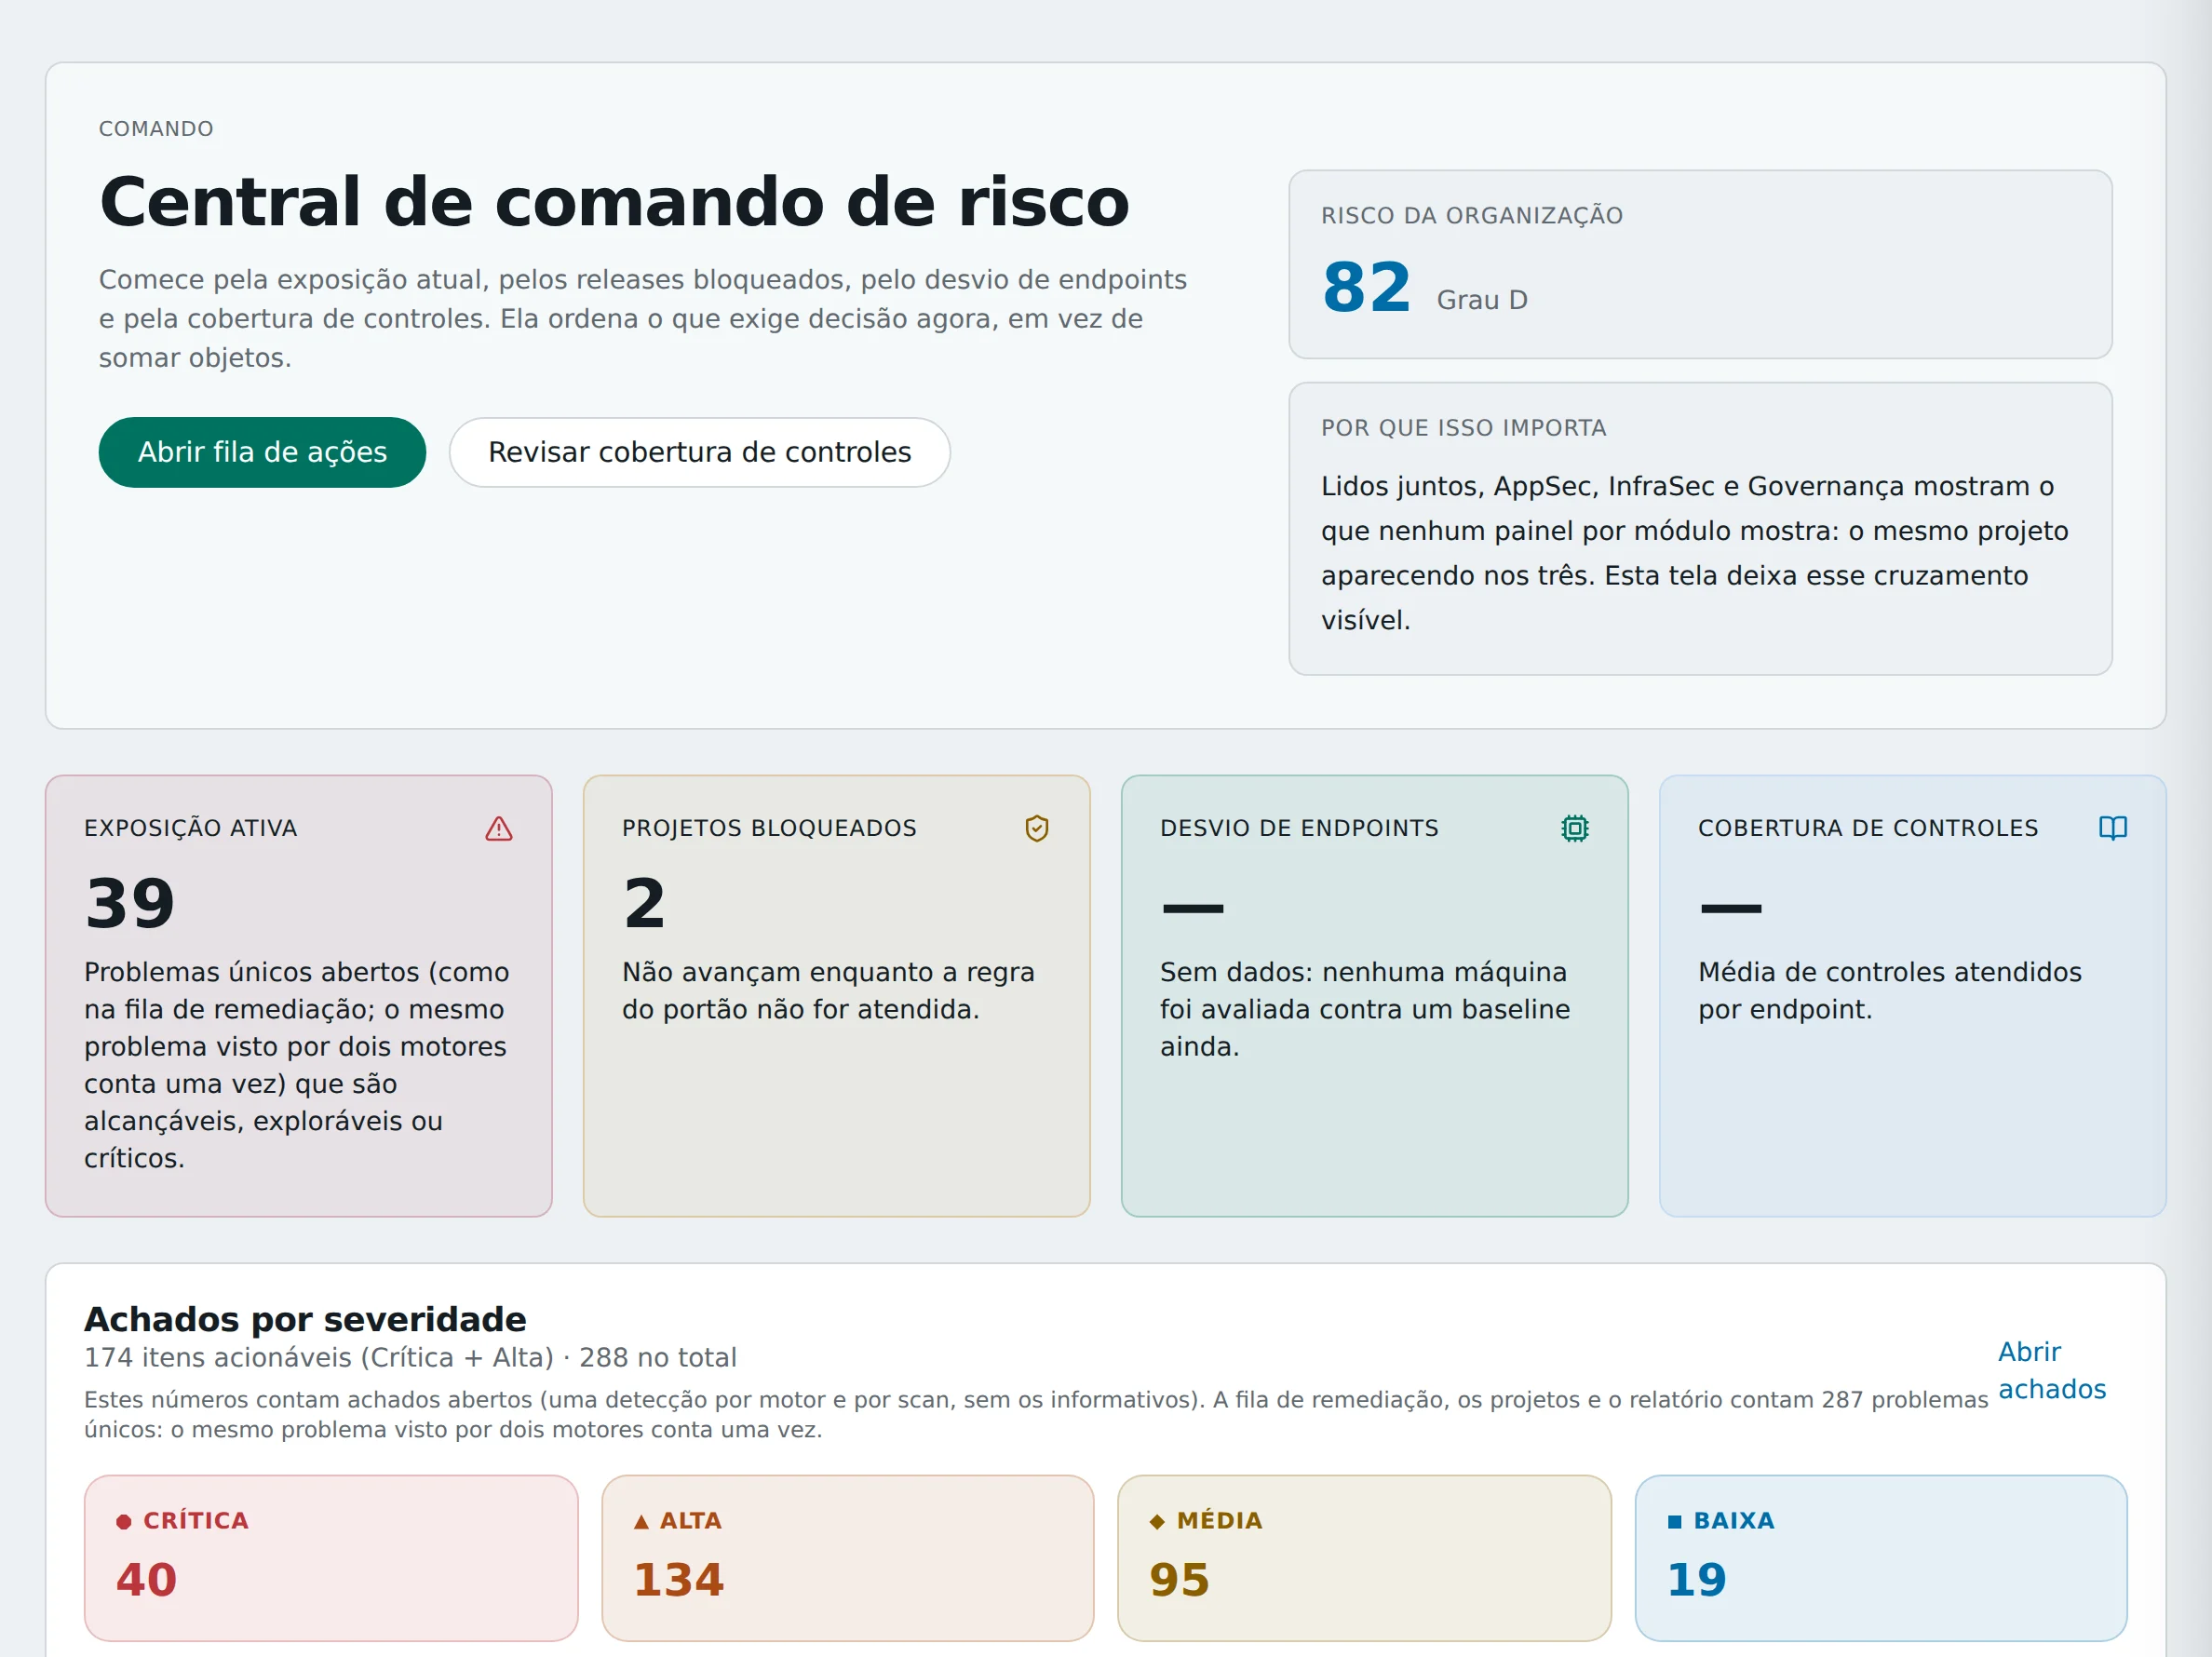
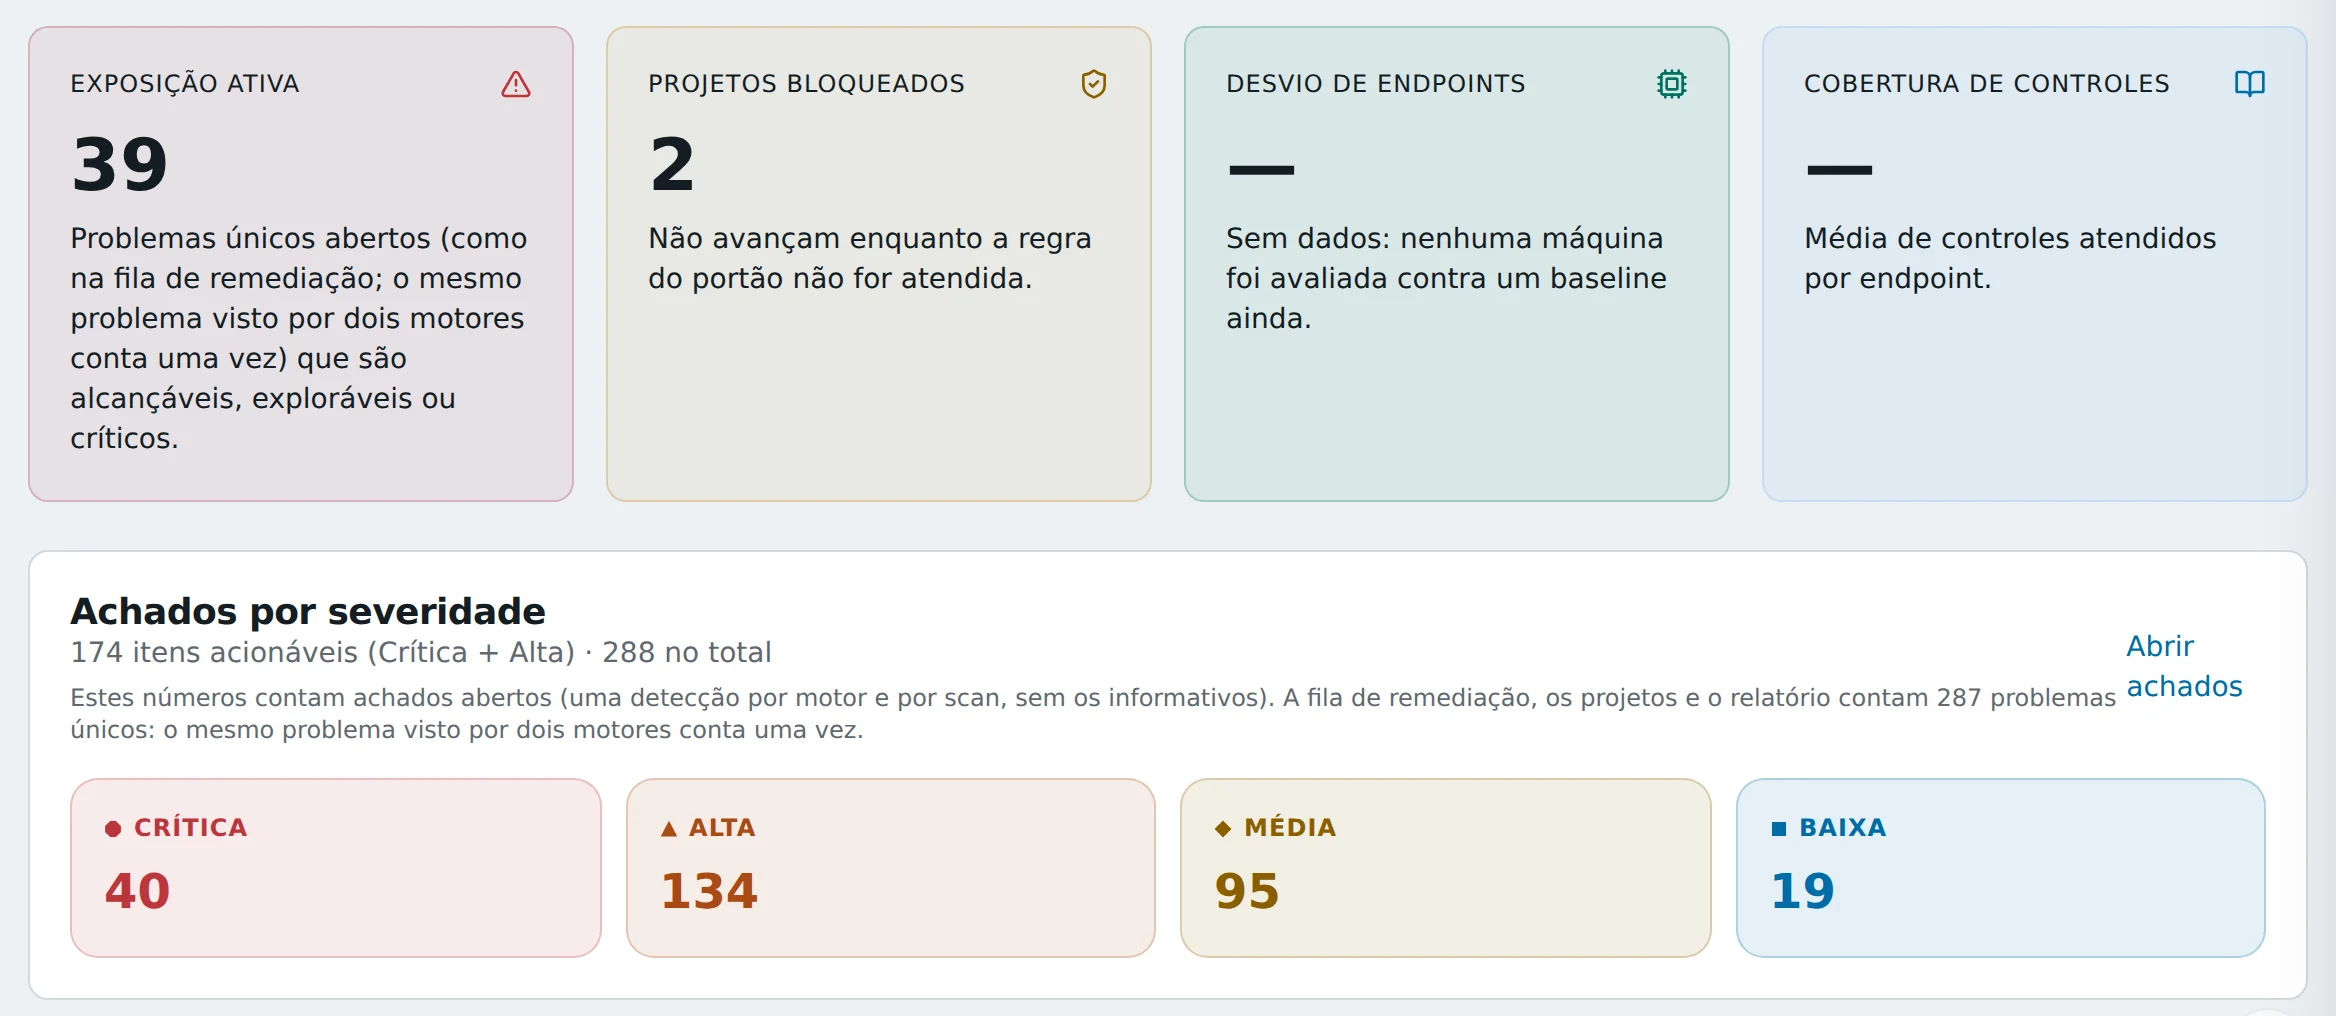
- The organization risk score, from 0 to 100, with its grade. This is the number the board follows.
- Active exposure: open problems an attacker can reach or exploit.
- Blocked projects: software versions that do not ship until the rule is met.
- Findings by severity, from critical to low. The analyst starts with the critical ones.
Who we are
CyberArmor is the Hegeon platform. Hegeon consulting runs the projects and delivers the work on it.
The analysts follow your company’s policies at every step of the work.
- Each project has an assigned analyst who answers for the work from start to finish.
- Every deliverable is on the platform, with the date it was done.
- The résumés and certifications of the assigned team are presented in the proposal.
Talk to a specialist for 30 minutes.
Tell us what your company needs. You leave the call with three priorities for your environment.
Prefer to write? Use the email contato@cyberarmor.com.br.